Systems Overview · 1995
FIREWALL (firewall)
The security gateway protected the central servers and the office LAN, with a separate policy on each interface. Dial-up customers were on the world/backbone side and were not the object of its protection.
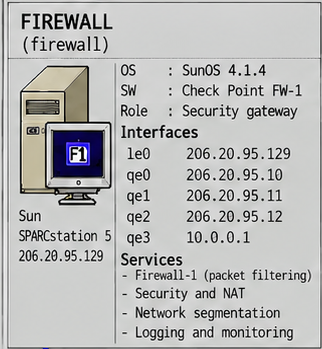
images/internetforce_server_map.png (Systems Overview 1995).System identity
- Hostname
firewall- Addresses
10.0.0.1(fw-world) ·206.20.95.10(fw-data) ·206.20.95.11(fw-users) ·206.20.95.12(fw-shell) ·206.20.95.129(office)- Platform
- Sun SPARCstation 5
- OS
- SunOS 4.1.4
- Role
- Check Point FireWall-1 gateway: packet filtering, NAT and segmentation.
Services and configuration
| Service / role | Description | Configuration / evidence | Documentation |
|---|---|---|---|
| FireWall-1 2.0a | Security gateway: packet filtering, NAT and network segmentation. | checkpoint/firewall-lic.txt · checkpoint/ | Security · TECHNICAL |
| Policy / rule base — visual evidence | Original Rule Base Editor screenshot (/usr/local/etc/fw/conf/final1.W), 15 rules. |
checkpoint/FW-policy.gif | Security |
| Routing and interfaces | Five Ethernet interfaces, host-specific routes on the DATA/USERS segments, POP routes. | network/rc.route · network/ | Architecture overview |
| Startup, logging and monitoring | FireWall-1 startup (fwstart), dial-up accounting, central loghost. |
network/rc.local | Monitoring |
| System hardening | Permission script, service accounts, minimal inetd, ftpusers. |
system/ · system/fixperms · ../users/system/ftpusers | Security |
FireWall-1 visual policy evidence
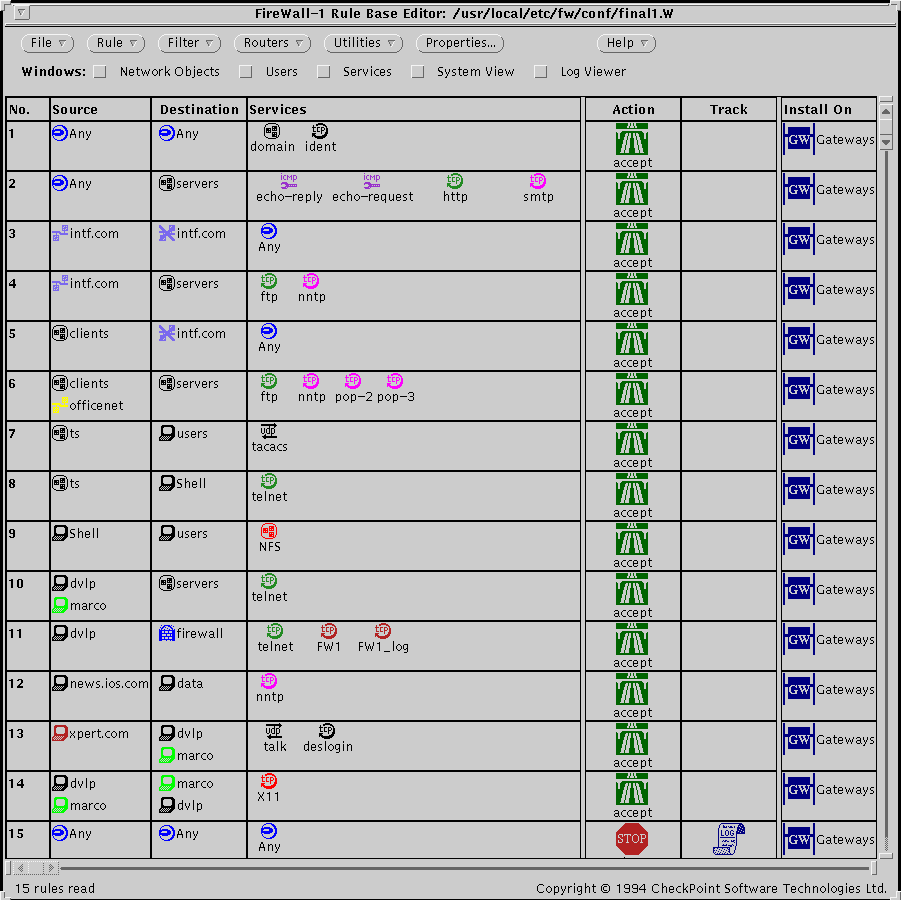
This original Rule Base Editor screenshot is visual evidence of the loaded policy, preserved as an artifact. It does not replace the textual transcript of the rules in Security, which remains the primary source.
On the maps
Full technical documentation
Open the canonical firewall README
This HTML page is a compact presentation; the Markdown README is the canonical source.